
01
Vulnerability assessment
Structured examination of networks, applications and devices to establish what is actually exposed, not what is assumed to be.
Cyber Keen tests what is exposed, watches what moves, and proves what happened across networks, applications, devices and the physical layer.
Assess
Find what is exposed
Detect
Watch what moves
Prove
Establish what happened
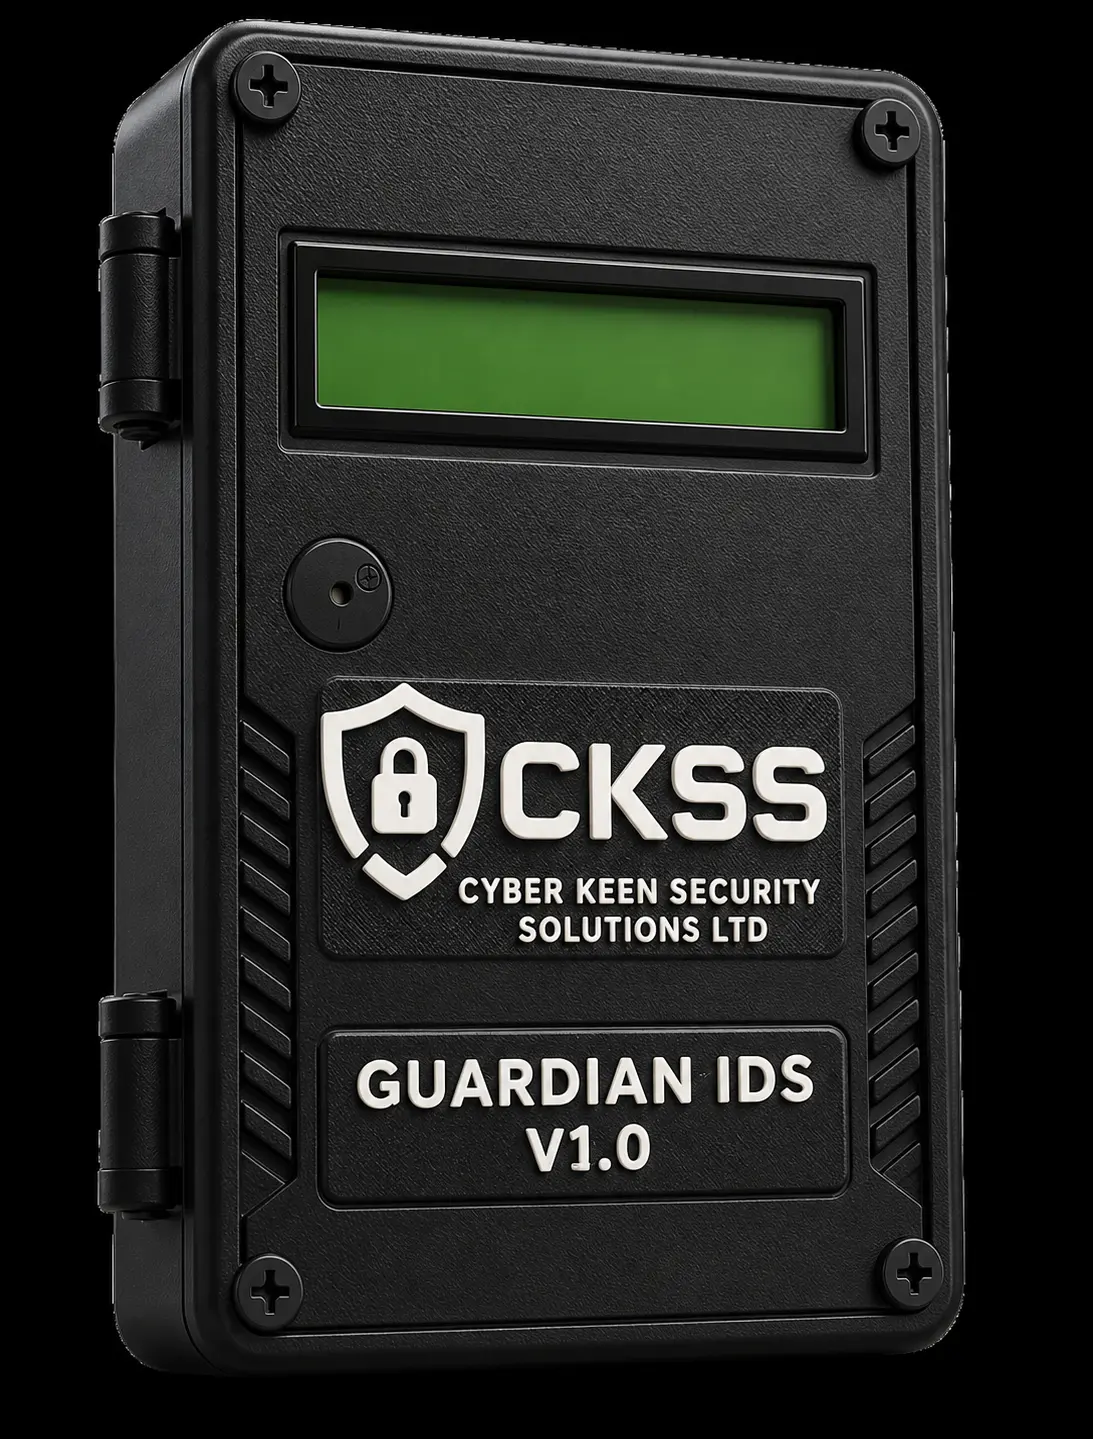
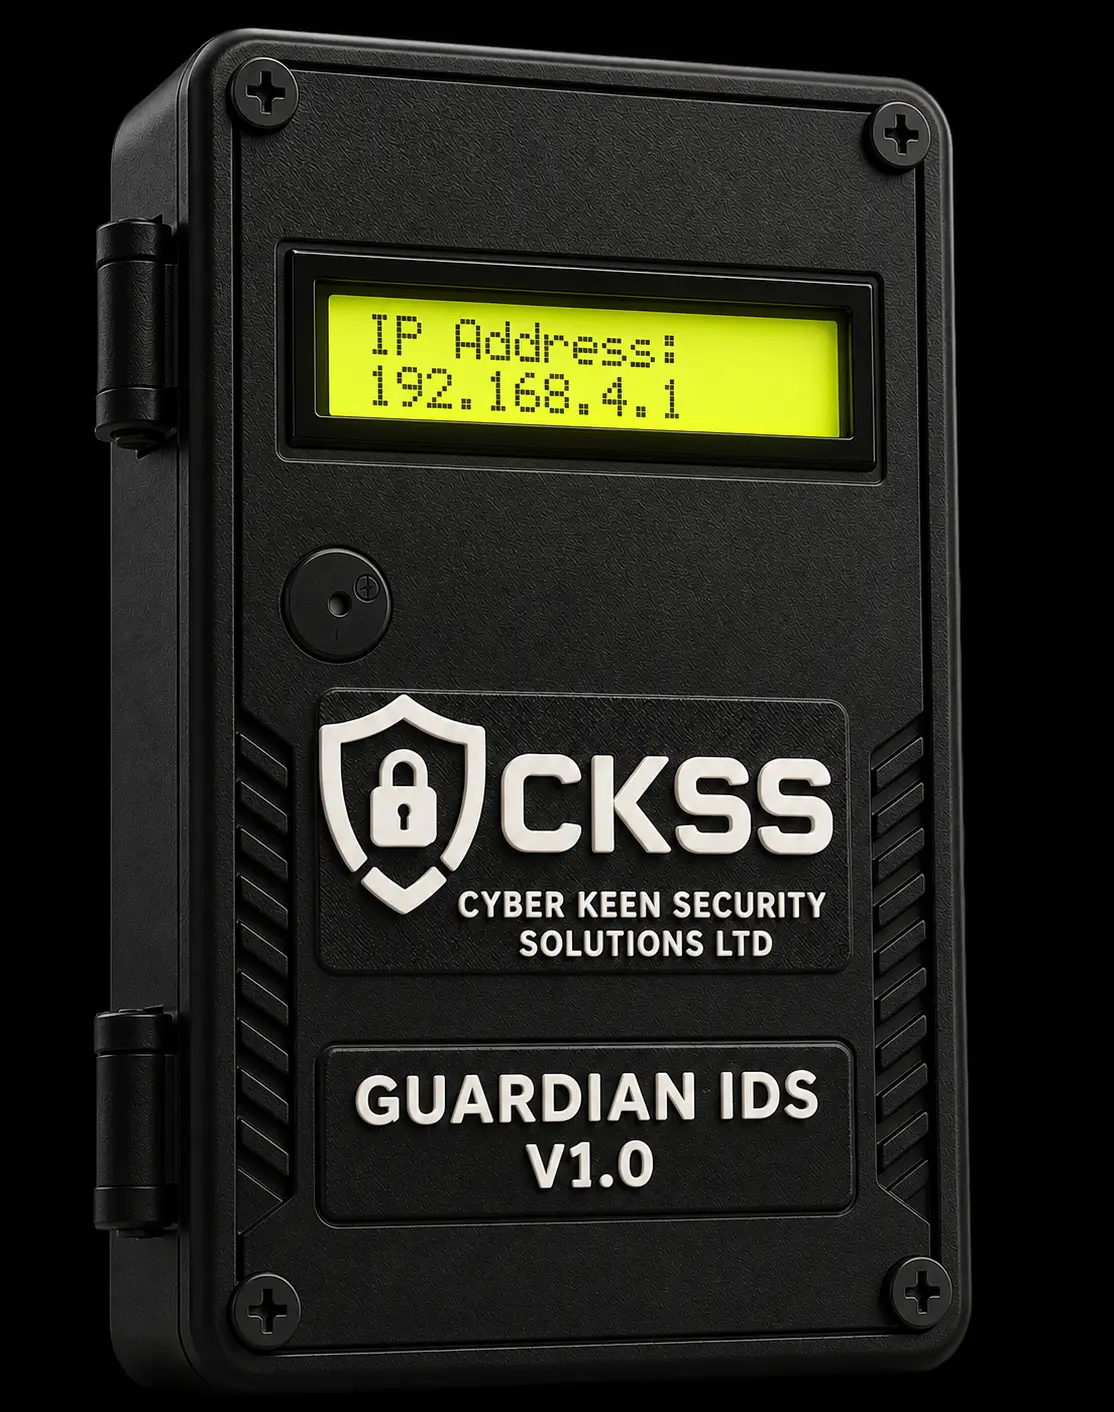
A short walkthrough of the physical unit, designed and assembled in-house.
Explore Guardian IDSFind what is exposed, prove which exposures matter, and hand over a remediation order that a technical team can actually work through.
Continuous observation of the estate with detection rules written for your environment rather than a generic template.
Establish what happened, how it was possible, and what can be evidenced, in a form that survives internal, regulatory or legal scrutiny.
Practical instruction for the people who actually hold the risk, staff, technical teams and leadership, using real scenarios rather than slideware.
Sound acquisition, methodical examination and defensible reporting of digital evidence from computers, mobile devices, servers and network data.
Each capability stands on its own, and each one feeds the others. Findings from an assessment shape detection logic; forensic work rewrites what we test for next.
Structured examination of networks, applications and devices to establish what is actually exposed, not what is assumed to be.
Controlled exploitation of confirmed weaknesses, so severity is demonstrated rather than estimated.
Continuous observation of network and system activity, with detection logic tuned to the environment being watched.
Acquisition and examination of digital evidence under a documented, repeatable chain of custody.
Reconstruction of how an incident occurred, who was involved and what can be evidenced.
In-house development of detection systems, including Guardian IDS V1.0, designed, built and maintained by Cyber Keen.
Acquisition, examination and reporting follow a documented sequence. Every step is repeatable, attributable and defensible under challenge.
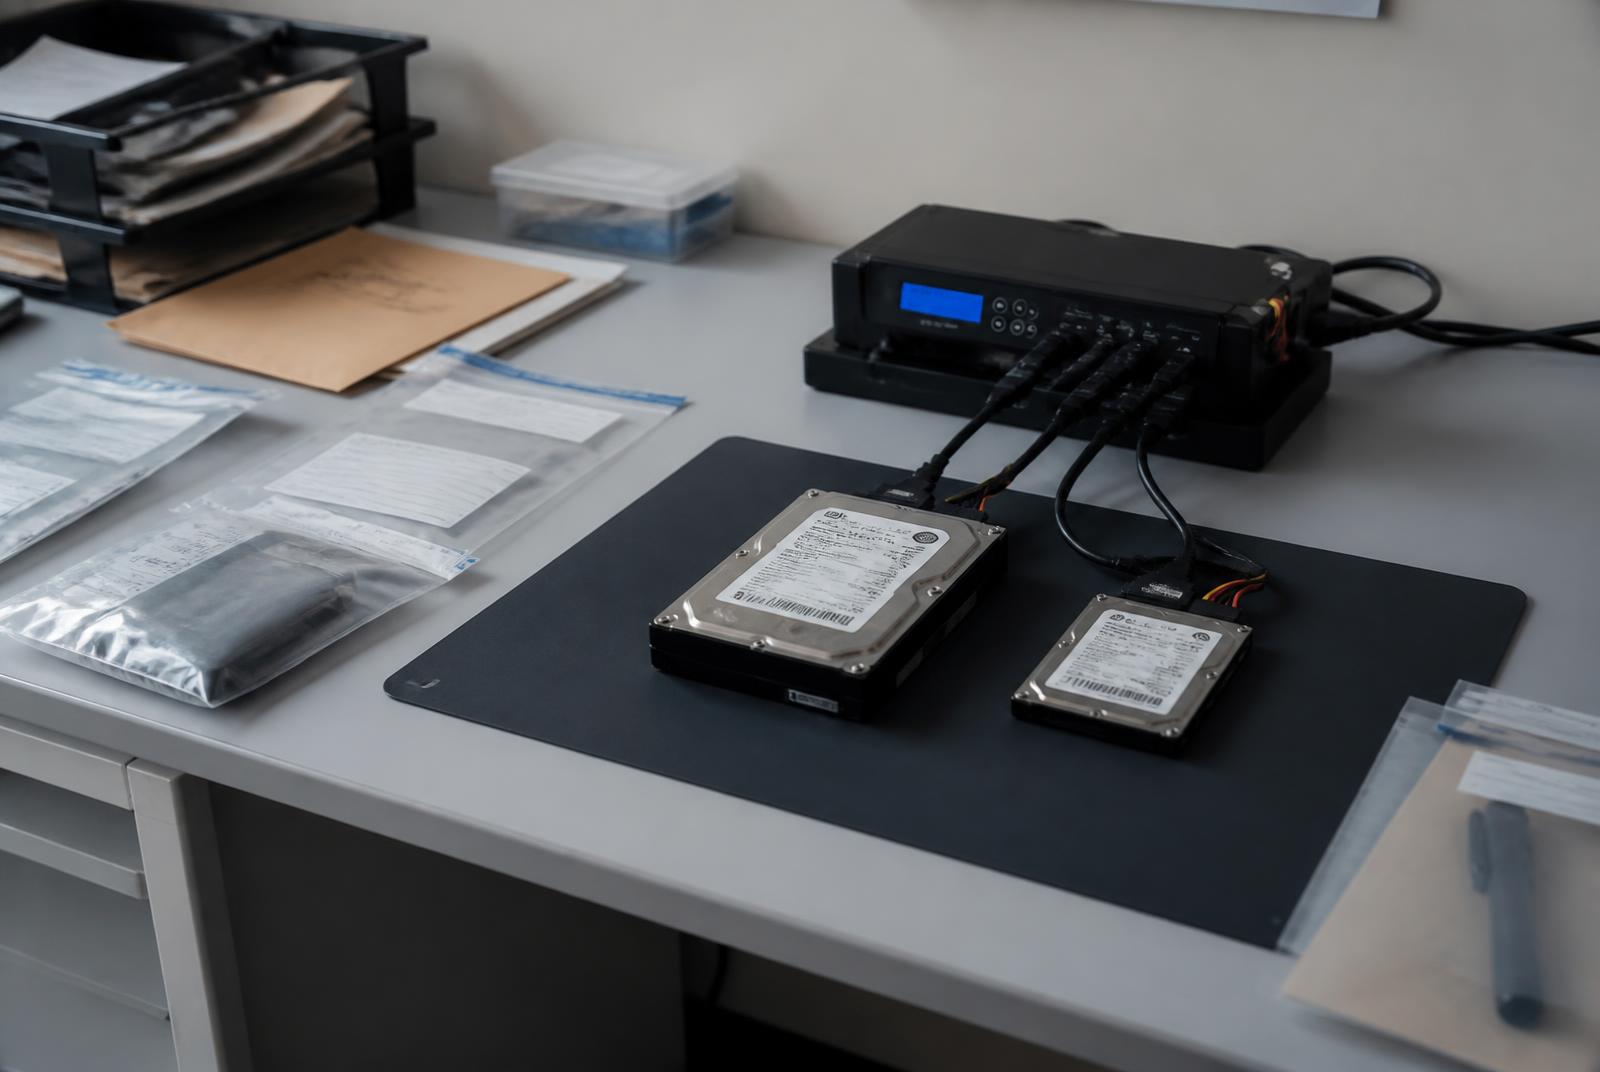
Establish which systems, devices and accounts hold relevant data, and secure them before anything changes.
Isolate the sources and record the chain of custody from the first moment a device is handled.
Create verified forensic images with write protection, and confirm integrity by hash before examination begins.
Work only on copies. Recover artefacts, deleted material and activity traces using documented methods.
Correlate the artefacts into a timeline and separate what the evidence shows from what it merely suggests.
Present findings, method and limitations in language a non-technical decision maker can act on and a specialist can audit.
Locked systems, an intrusion in progress, or an account takeover? Reach Cyber Keen directly and tell us what is happening.
An intelligent detection system developed in-house, hardware, firmware and detection logic built by Cyber Keen rather than assembled from a reference design. V2 is already in development.
Hardware, firmware and detection logic developed by Cyber Keen rather than assembled from a reference design.
Activity is evaluated against behaviour observed in the deployed environment, not a fixed signature list alone.
Detections are raised with the context needed to decide, so an alert is a decision point rather than noise.
The team that built the system tunes and supports it after deployment.
V2 builds on V1's proven real-time threat detection with smarter analysis, improved visibility and lightweight AI-assisted network monitoring.
Payment-rail fraud in financial services, operational technology in energy, patient data in healthcare: each engagement is scoped to what that sector's systems actually expose.
 Financial services
 Government
 Telecommunications
 Healthcare
 Education
 Energy
 Retail and e-commerce
 Logistics
Each badge below only shows as verified once the matching certificate has been uploaded and published, not before.
EFCC / SCUML
Special Control Unit Against Money Laundering registration.
Not uploadedCAC
Corporate Affairs Commission incorporation.
Not uploaded
Trademark
Registered trademark for the Cyber Keen name and mark.
Not uploadedNDPR
Nigeria Data Protection Regulation compliance.
Not uploadedNDPC
Nigeria Data Protection Commission registration.
Not uploadedThe people who scope the work are the people who sign the report.
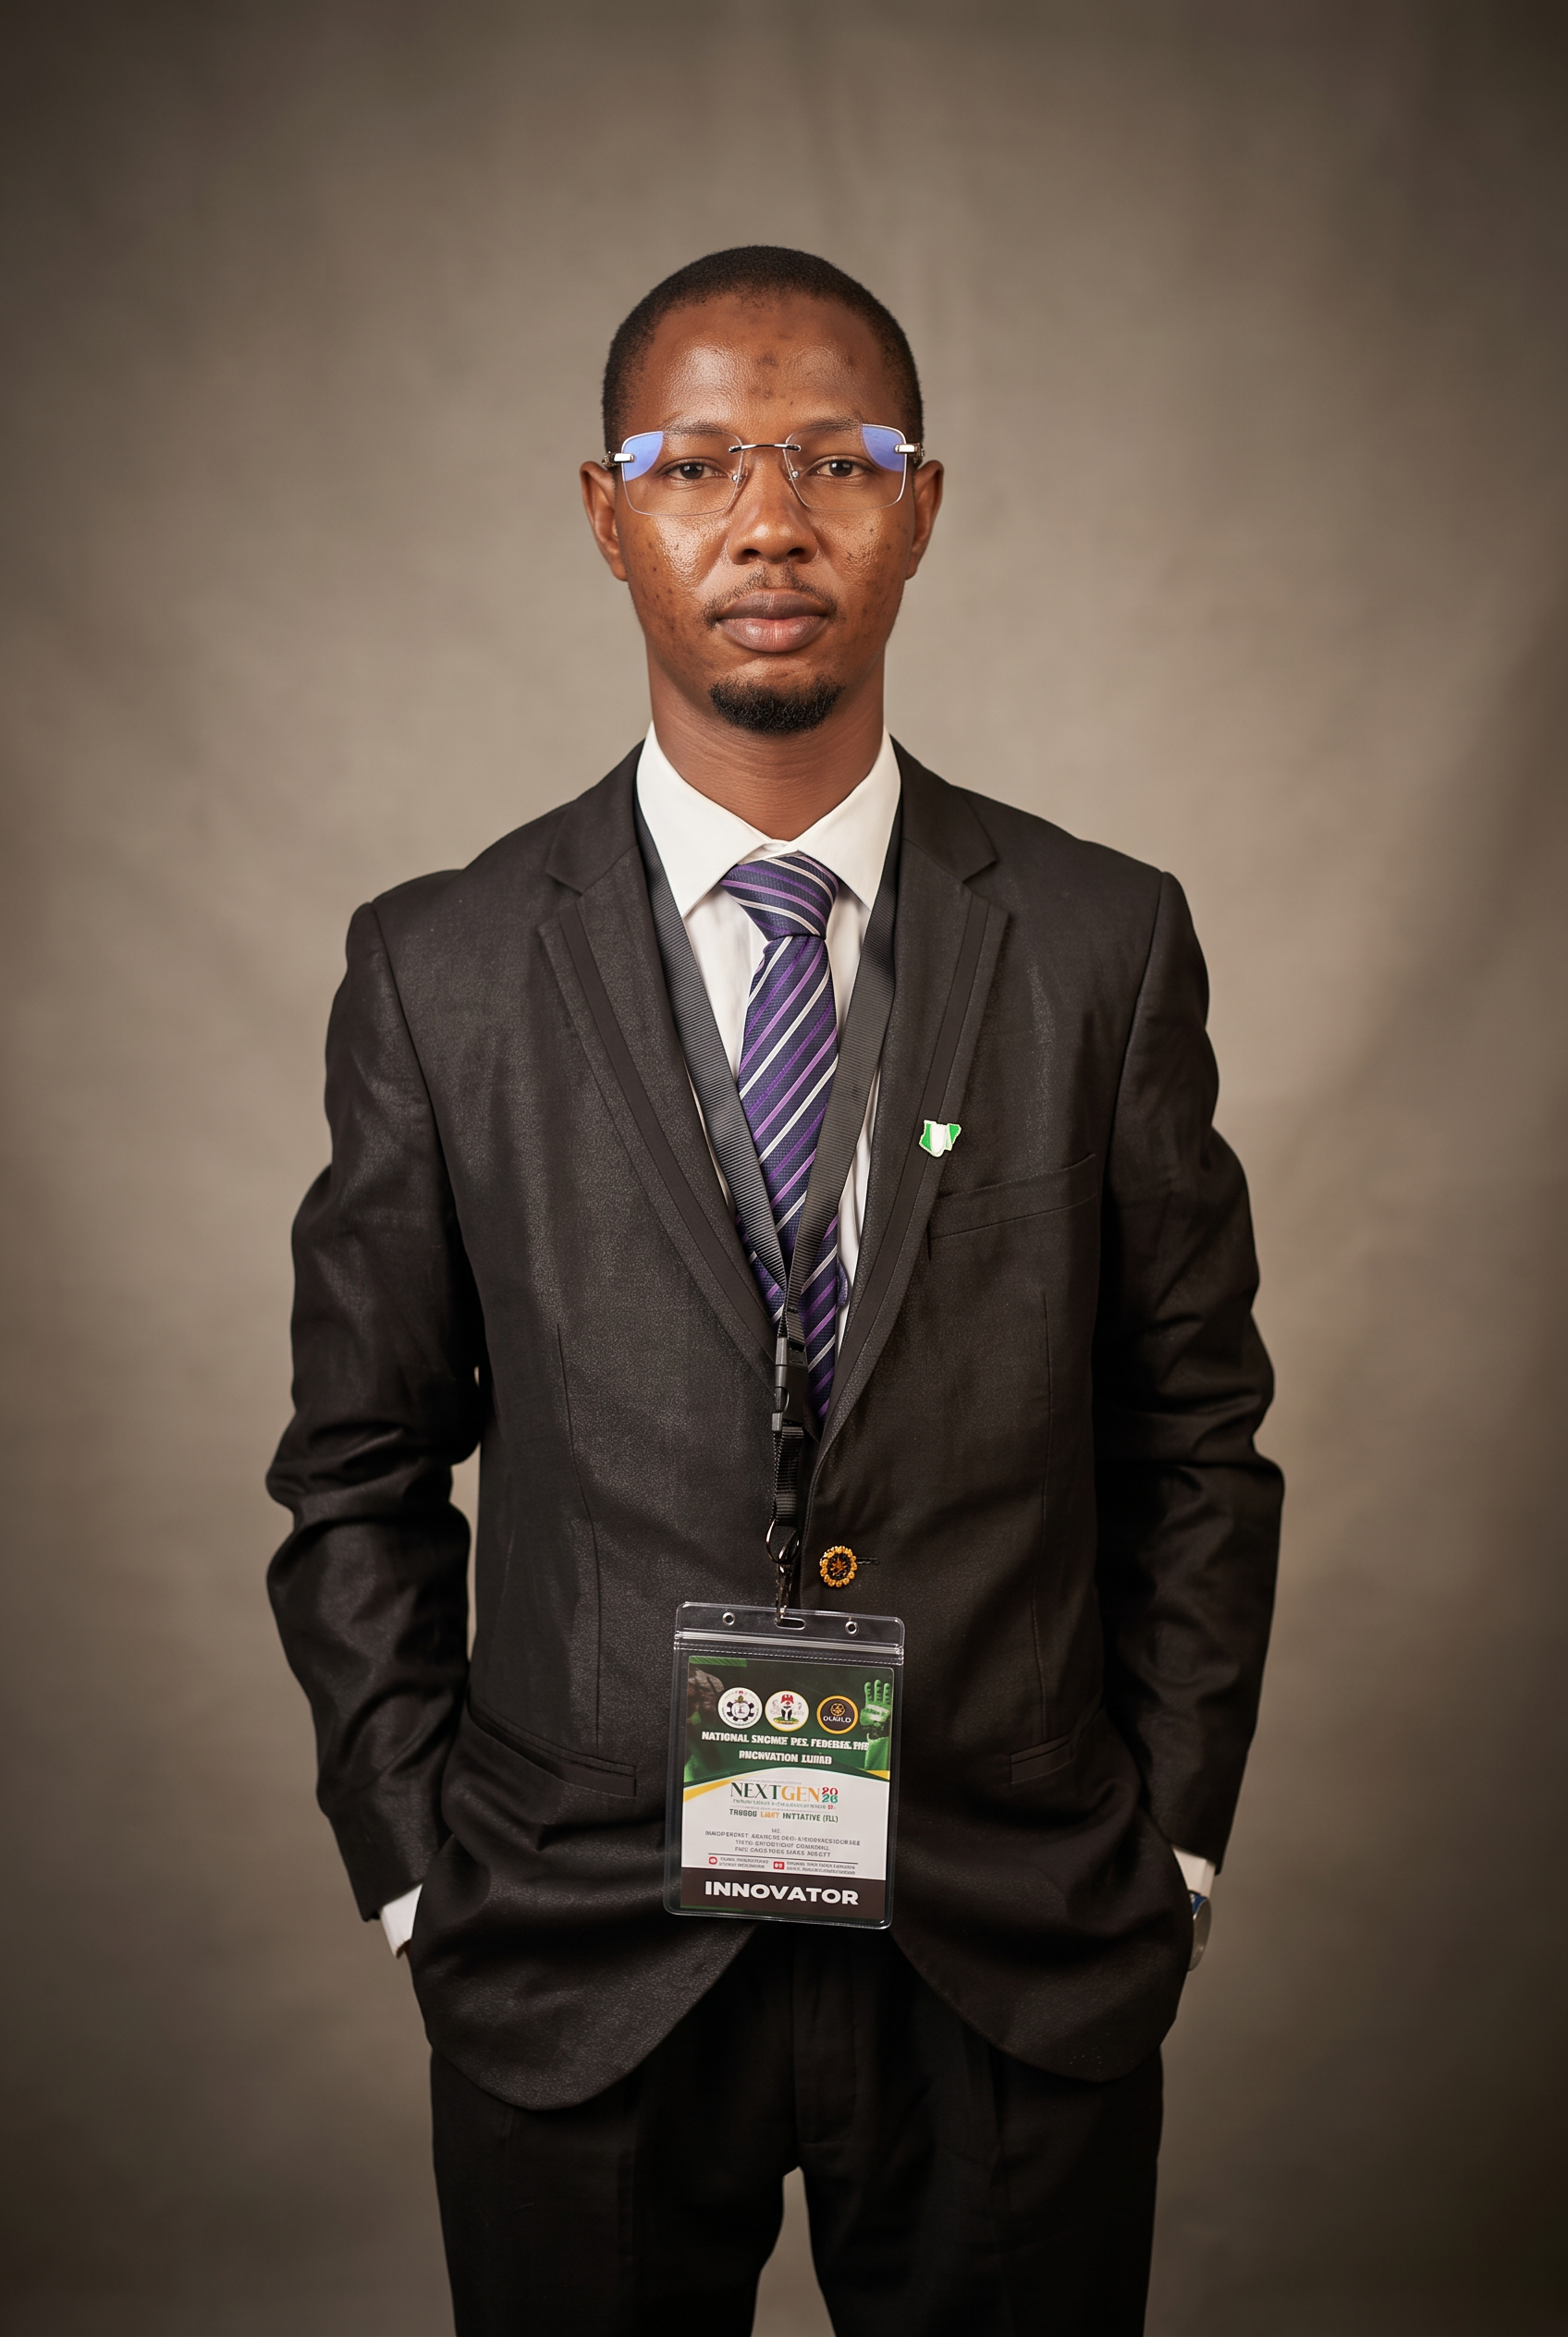
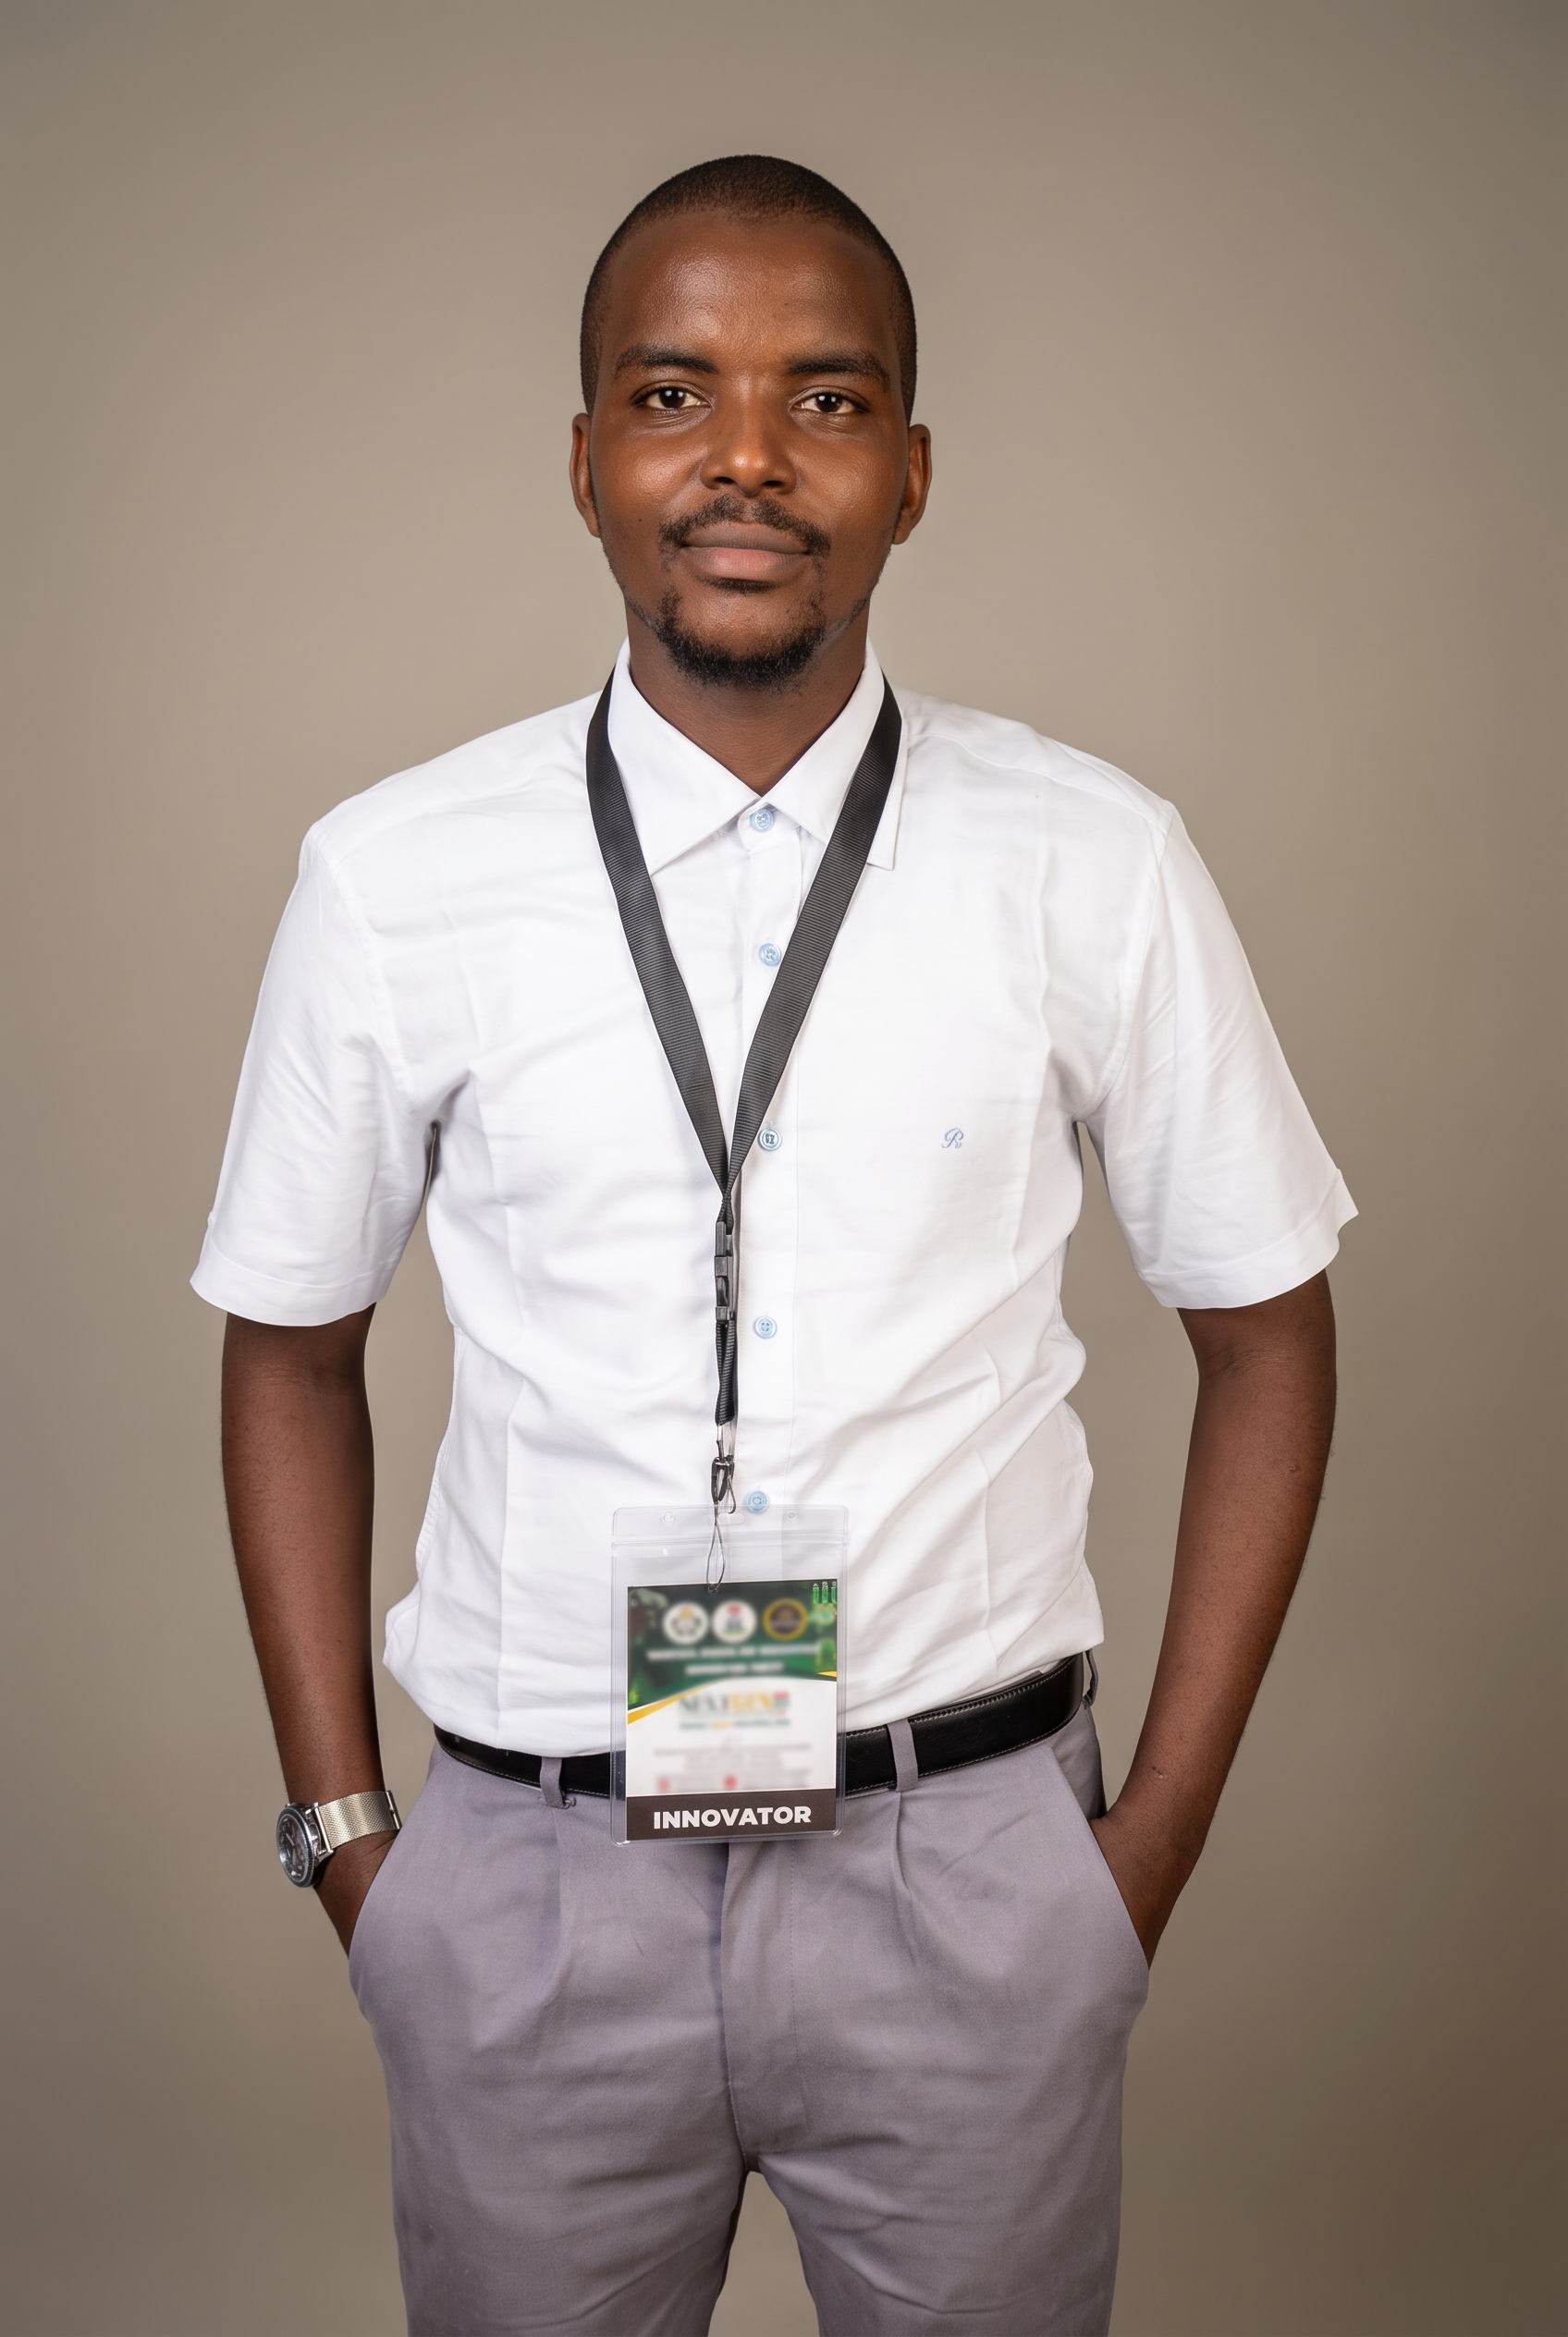
Founder & Chief Executive Officer
Abdullahi Umar Abbas is the Founder and Chief Executive Officer of Cyber Keen Security Solutions Ltd, with a professional background in cybersecurity and a strong focus on Vulnerability Assessment and Penetration Testing (VAPT). His expertise includes identifying security weaknesses, assessing cyber risks, and strengthening digital systems through practical security testing and defensive cybersecurity practices.
LinkedInDragScrollHover or arrows
Every engagement starts with scope, not a quotation. We would rather understand the estate first and tell you plainly which work is worth doing.
Contact Cyber Keen