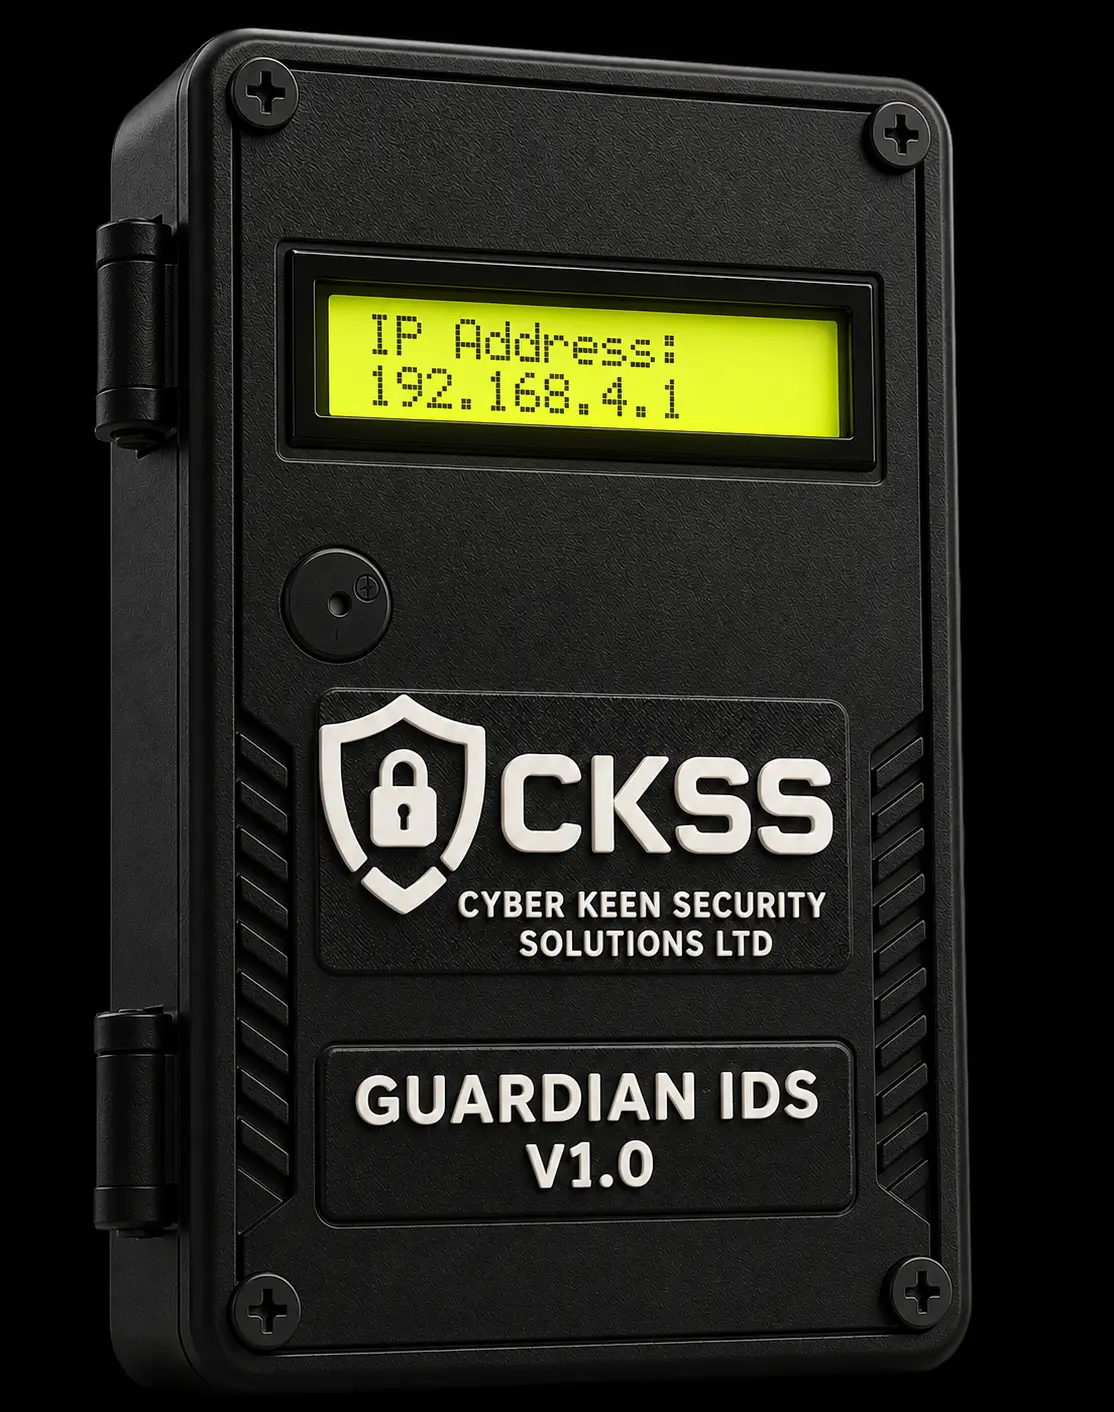
Designed in-house
Hardware, firmware and detection logic developed by Cyber Keen rather than assembled from a reference design.
An intelligent detection system built by Cyber Keen, hardware, firmware and detection logic developed together rather than assembled from a reference design.
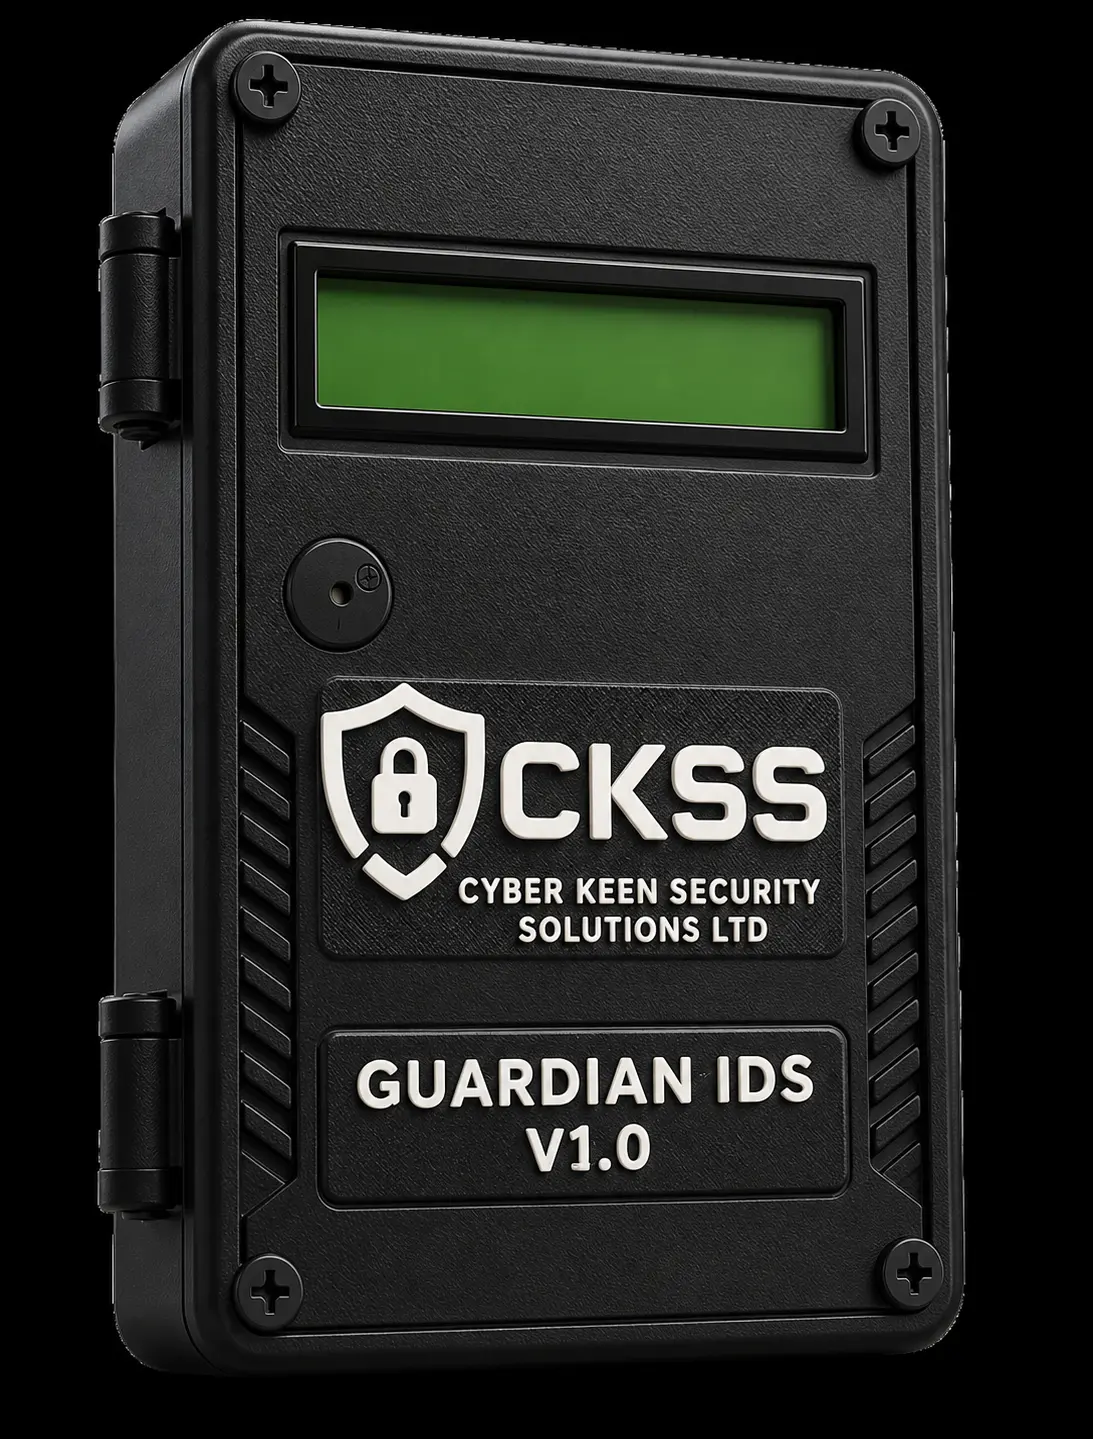
Drag to rotate
Hardware, firmware and detection logic developed by Cyber Keen rather than assembled from a reference design.
Activity is evaluated against behaviour observed in the deployed environment, not a fixed signature list alone.
Detections are raised with the context needed to decide, so an alert is a decision point rather than noise.
The team that built the system tunes and supports it after deployment.
Each stage is inspectable. Where the system is uncertain, it says so rather than guessing.
The ESP32-based unit watches Wi-Fi and Ethernet traffic for rogue access points, unfamiliar devices and deauthentication attempts.
Stage 01 of 05Captured traffic is structured into a consistent internal format the detection logic can evaluate.
Stage 02 of 05Activity is checked against expected behaviour, including ARP spoofing, port scanning and Wi-Fi evil-twin patterns.
Stage 03 of 05A confirmed detection triggers an instant email alert and shows on the unit's onboard LCD, so it reaches someone straight away.
Stage 04 of 05Outcomes feed back into tuning, so detection improves with use.
Stage 05 of 05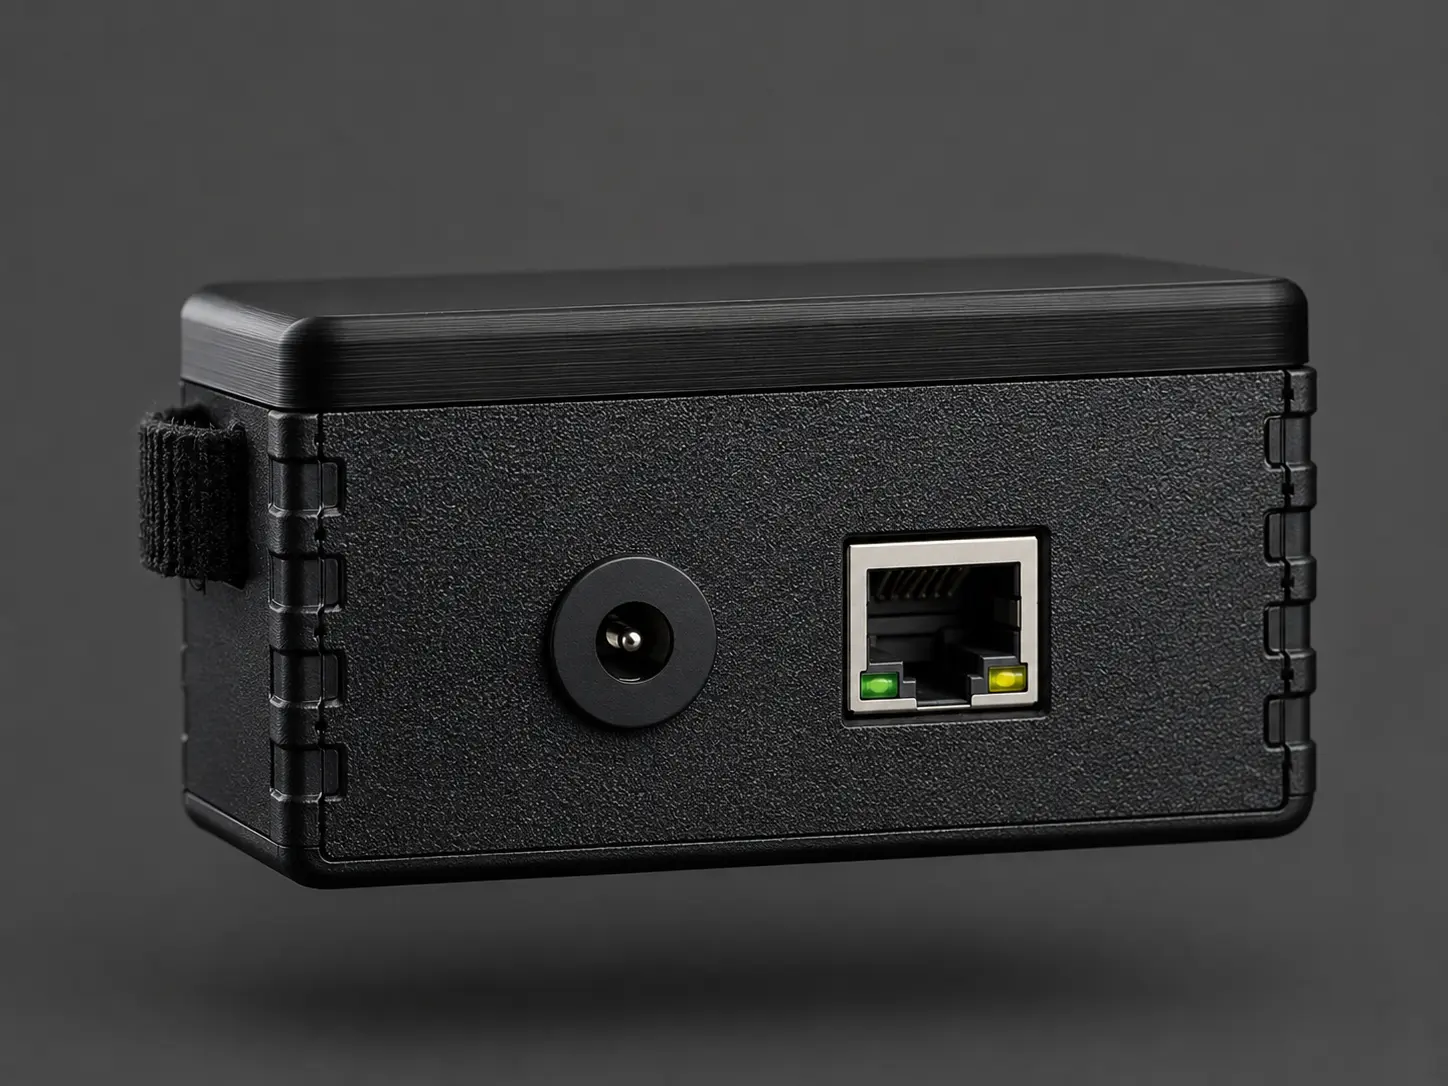
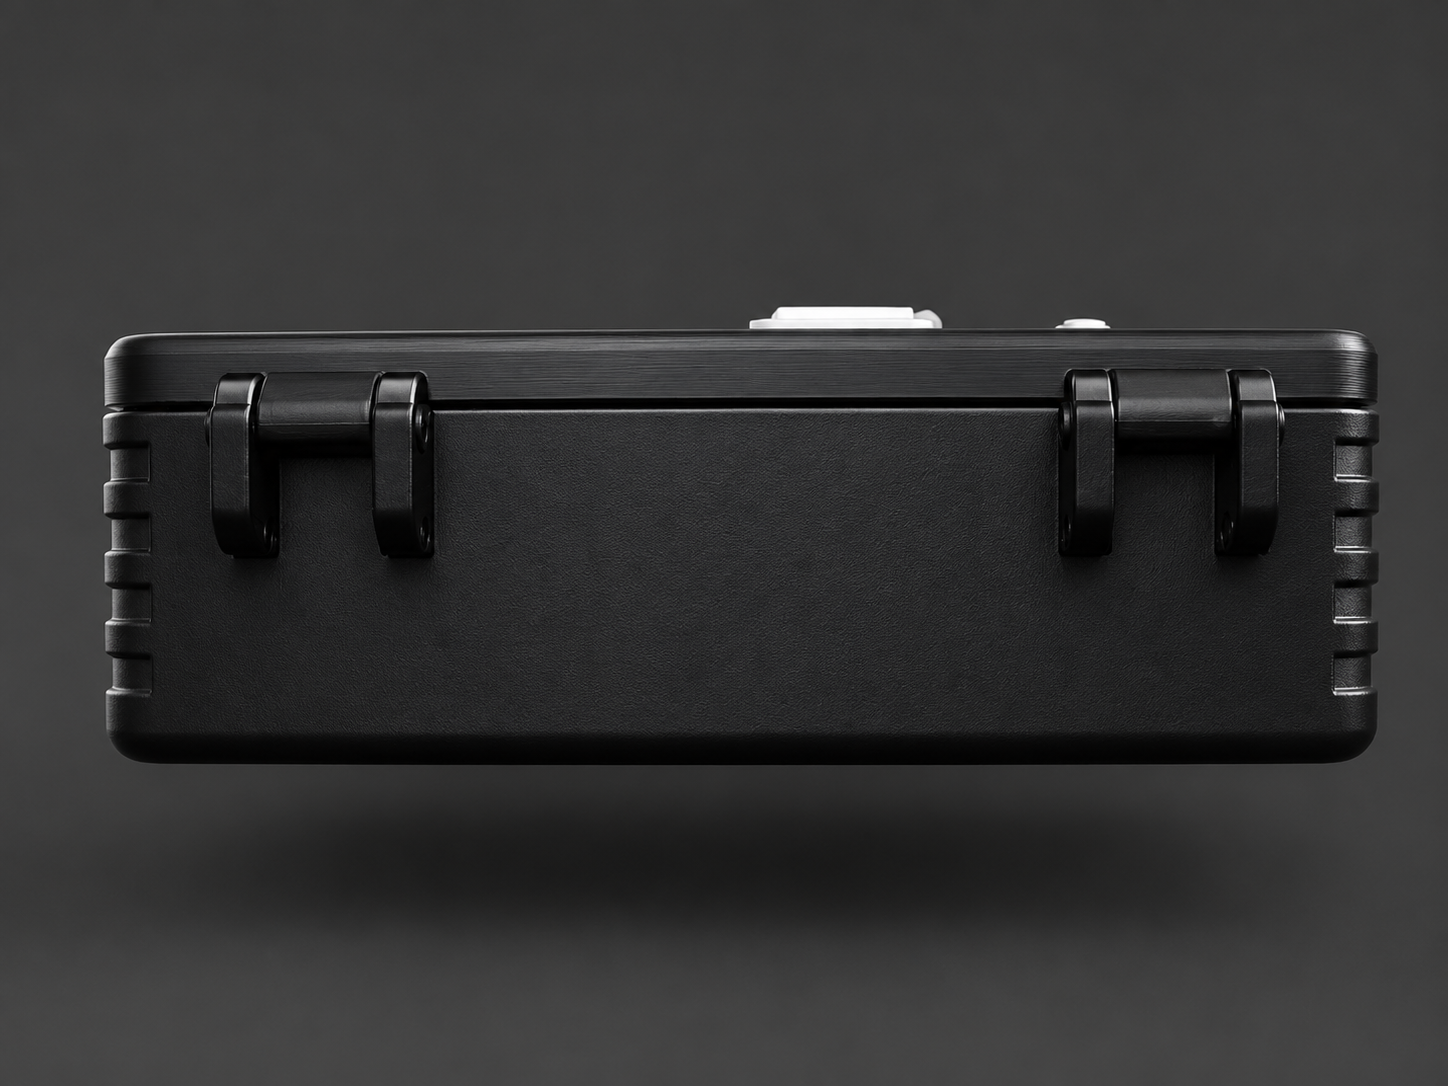
Confirmed details appear below. Where a figure has not been measured and confirmed, we say so rather than estimate it.
We assess whether Guardian IDS V1.0 suits the site before proposing it, and say so when it does not.
Request a briefing